

If you’ve ever wondered how dozens of devices in your office or school can all access the internet using just one or a handful of public addresses, you’ve bumped into Network Address Translation, or NAT. Think of NAT like a busy receptionist at a large company building. Everyone inside the building has their own internal extension number, but when they call outside or receive calls from the public, the receptionist handles the translation to the main company phone number. This keeps things organized inside while presenting a simple face to the outside world.
NAT is a fundamental feature in almost every firewall and router today. It’s especially important in enterprise firewalls from vendors like Fortinet (FortiGate), Sophos, and Cisco. In this post, we’ll break down why NAT exists, how it works at a high level, and key concepts you’ll run into when configuring or troubleshooting it.
Why NAT is Needed in the Modern Internet
The internet runs on IP addresses – those unique numbers that identify every device connected to the network. The version most of us still use, IPv4, only has about 4.3 billion possible addresses. That sounded like plenty back in the 1980s, but with billions of smartphones, computers, IoT devices, and servers now online, we’ve run out.
NAT was invented as a clever workaround. It lets thousands of devices share a small number of public (globally unique) IP addresses. Without NAT, schools and small-to-medium businesses would need to buy huge blocks of public addresses – expensive and wasteful. Instead, devices inside your network use “private” addresses that aren’t routable on the public internet. The firewall translates them on the fly.
This not only conserves addresses but adds a layer of security by hiding your internal network layout from the outside world.

Why Understanding NAT Basics is Critical for Troubleshooting
When internet access breaks – slow connections, certain sites not loading, or remote access failing – NAT is sometimes the culprit. Misconfigured translations can block traffic, cause asymmetric routing (where requests go one way but replies take another), or exhaust port resources.
In firewalls, NAT rules interact closely with security policies. A packet might pass the firewall rules but fail because the translation doesn’t match. Logs often show “no translation” errors. Knowing the basics helps you quickly check if source addresses are being hidden properly, if ports are overloading, or if a server needs a fixed mapping.
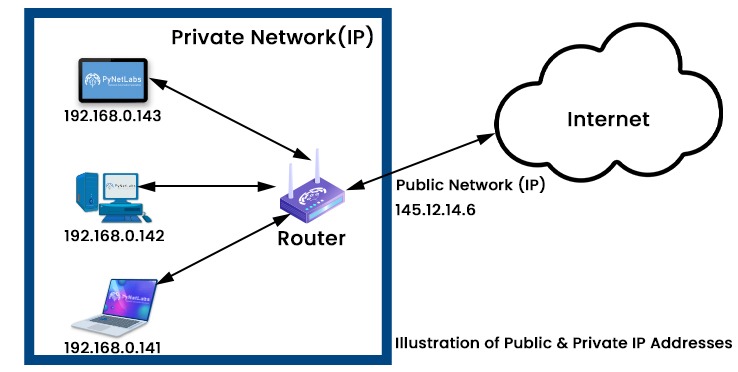
Private and Public IP Addresses
Public IP addresses are globally unique and routable on the internet – like a street address anyone can use to find your building.
Private IP addresses are reserved for internal use (from RFC 1918 ranges like 10.0.0.0/8, 172.16.0.0/12, and 192.168.0.0/16). They’re not routable outside your network – like internal office phone extensions. Devices with private addresses can’t directly talk to the internet without translation.
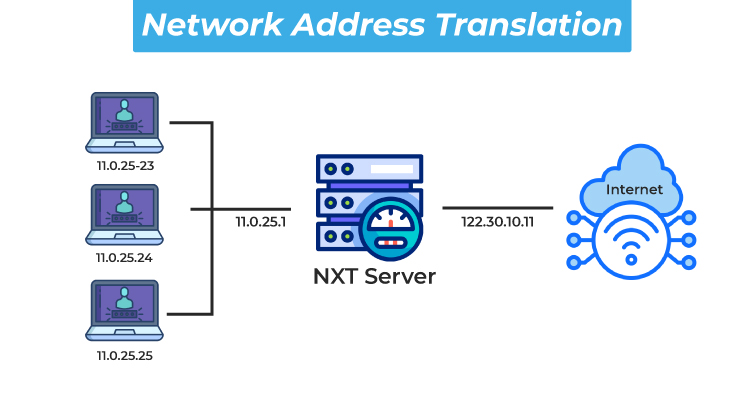
The firewall sits at the border, swapping private for public (and vice versa) as needed.
Source Address and Destination Address
Every internet packet has two key IP fields:
- Source address: Where the packet is coming from.
- Destination address: Where it’s going.
For outgoing traffic (internal network —> to internet), NAT typically changes the source address from private to public.
For incoming traffic (internet —> to internal network), NAT changes the destination address from public to private.
This bidirectional swap is what makes conversations work seamlessly.
How NAT Translation Works at a High Level
Imagine your office network as a private club. When a member (device) wants to step outside:
- They hand their request to the doorman (firewall).
- The doorman notes the member’s internal details.
- He rewrites the request to show the club’s public address as the sender.
- The outside world replies to the club.
- The doorman looks up his notes and forwards the reply to the right member.
The “notes” are a translation table the firewall maintains. Entries time out if unused, freeing resources.

IP Ports and Why They’re Crucial in NAT
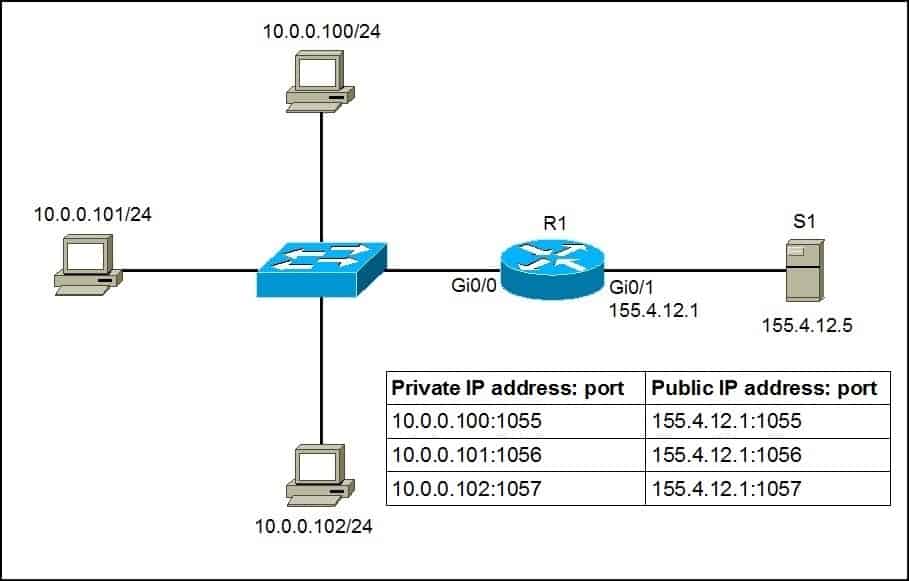
IP addresses identify devices, but ports identify specific conversations or services (like web browsing on port 80/443).
A single computer inside your network can have hundreds of simultaneous connections. When many computers such as student laptops share one public address, the firewall uses ports to keep things straight.
This is called Port Address Translation (PAT), or overload. The firewall rewrites not just the IP but also the source port to a unique value. Replies come back to the public IP and that unique port, letting the firewall match them to the original private device and port.
Without ports, NAT would need one public IP per simultaneous connection – impossible for busy networks.
One-to-Many NAT
This is the most common setup, also called NAT overload or PAT. Many private devices share one (or a few) public addresses.
All internal devices hide behind the firewall’s public IP for outgoing traffic. Ports distinguish connections.
In Fortinet FortiGate: Use IP Pools with “overload” type or central SNAT.
In Sophos: Masquerading (SNAT to interface address).
In Cisco ASA/Firepower: Dynamic PAT (hide behind interface or a single address).
Perfect for general internet access in schools and businesses.
Many-to-Many NAT
Here, a group of private addresses translates to a pool of public addresses (dynamic NAT without port overload).
Each internal device gets a temporary public IP from the pool. Useful when you have more public IPs available and need true one-to-one for certain apps.
Less common today due to address scarcity; ports usually handle the load.
In Cisco: Dynamic NAT with a pool.
In Fortinet: Dynamic IP Pool (fixed port, no overload).
In Sophos: SNAT with a range.
NAT Pooling
A NAT pool is simply a group of public IP addresses the firewall draws from for translations.
- Overload pools: Add port translation (many-to-one per IP).
- Non-overload: One-to-one, exhausts faster.
Firewalls let you create pools for source NAT (outgoing) or even destination (incoming load balancing).
In Fortinet: IP Pools.
In Sophos: Translated source as a range.
In Cisco: NAT pools for dynamic translations.
NAT in Popular Firewalls: Fortinet, Sophos, and Cisco
- Fortinet FortiGate: Uses Virtual IPs (VIPs) for incoming (destination NAT, like port forwarding). Source NAT via policies (interface address) or IP Pools. Central NAT separates rules for clarity.
- Sophos: Linked or manual SNAT/DNAT rules. Masquerading for simple outbound. Assistants help create full setups (DNAT + reflexive SNAT).
- Cisco ASA/Firepower: Object-based NAT. Auto (per-object) or Manual (sectioned for precedence). Dynamic PAT common; static for servers.
All integrate NAT tightly with security policies – traffic must match both.
How Twotrees Technologies Can Help
At Twotrees Technologies, our engineers have extensive experience designing and troubleshooting large campus networks for schools and businesses. We’re certified partners with leading vendors like Fortinet, Sophos, Cisco/Meraki, and more, which means we’re deeply familiar with Network Address Translation configurations and best practices.
Whether you’re planning a new network, expanding an existing one, or stuck on connectivity issues that point to NAT problems, we can help. From initial design to ongoing management and rapid troubleshooting, our team ensures your network runs smoothly and securely.
Reach out to us today – we’d love to assist with your network design and troubleshooting needs.
NAT isn’t going away soon, even as IPv6 grows. It provides flexibility and that extra security-by-obscurity layer. Next time connectivity issues arise, check those translation tables first – it’ll save hours of head-scratching!


